Identify Web Vulnerabilities Simulate Attacks Secure Your Applications
Protect your web applications from real-world attacks with comprehensive penetration testing. We simulate attacker behavior to identify exploitable vulnerabilities, validate security controls, and provide actionable remediation guidance to strengthen your application's overall security posture.
What is Web Application Penetration Testing?
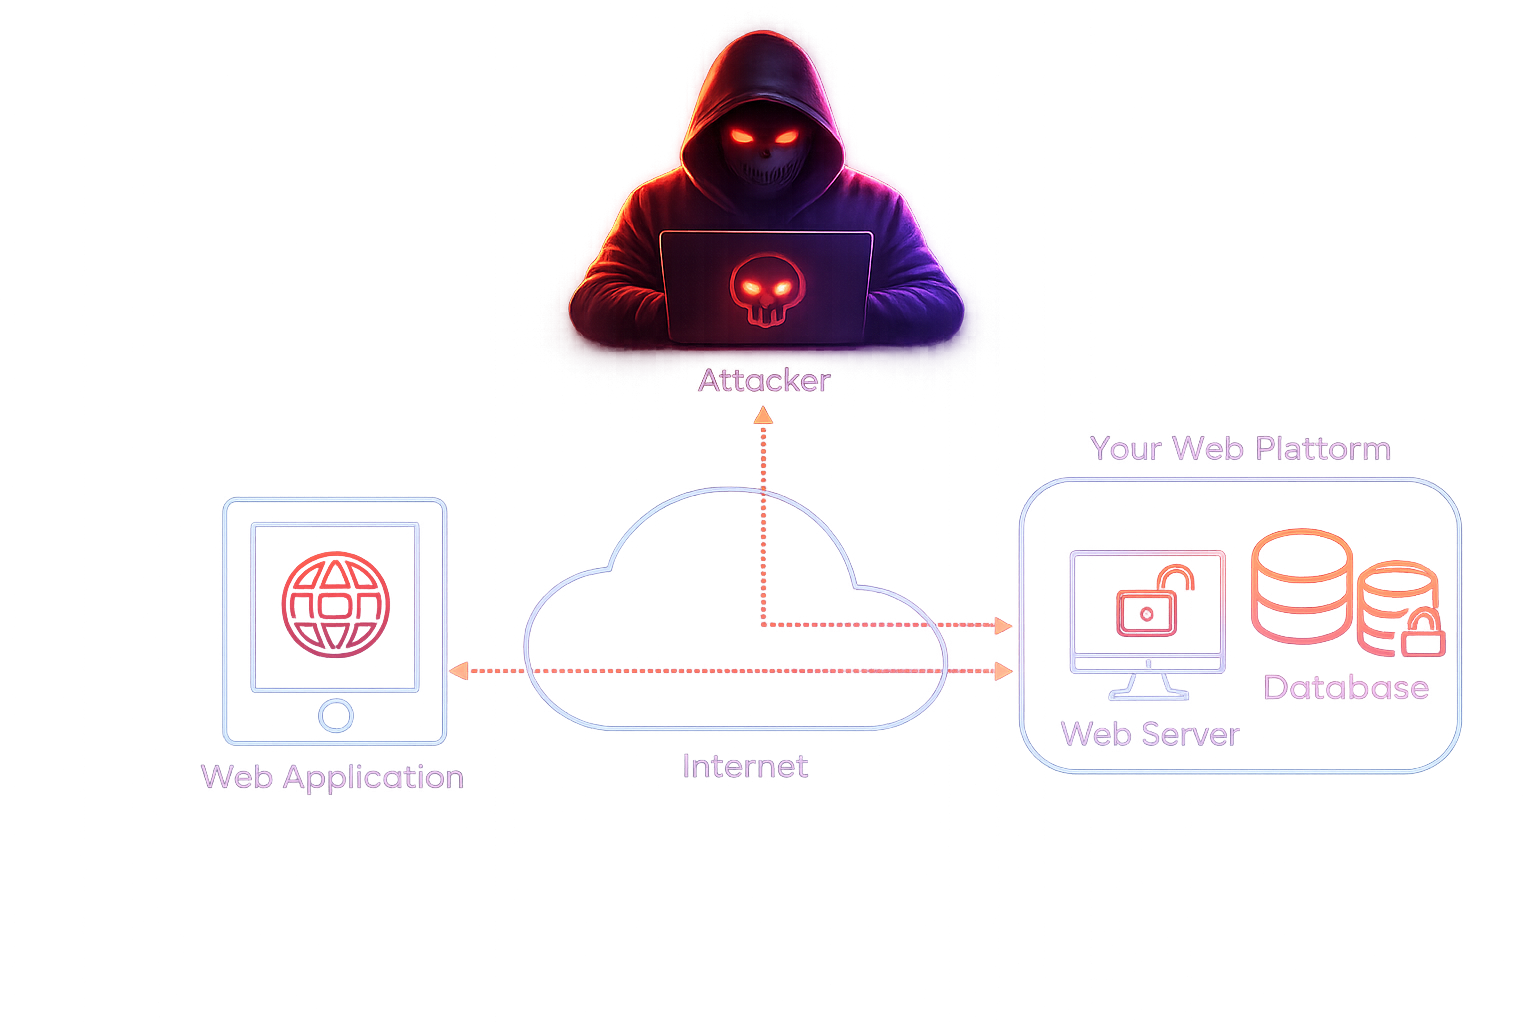
Web Application Penetration Testing (Web VAPT) is a comprehensive, hands-on security assessment that simulates real-world attacks against your online platforms — before adversaries exploit them.
Our certified experts manually probe every layer of your application: authentication, business logic, APIs, data flows, and session management. We go beyond automated scans to uncover the complex, chained vulnerabilities that tools consistently miss.
-
Strengthen User Trust A validated secure application signals reliability, building lasting confidence with your customers and partners.
-
Competitive Advantage Stand apart in a marketplace where security credentials directly influence procurement and partnership decisions.
-
Data Breach Prevention Remediate exploitable weaknesses before they result in regulatory penalties, litigation, and reputational damage.
-
Performance Optimization Security hardening often eliminates wasteful processes, improving application speed and reliability as a side effect.
Based on aggregated client assessment data · 2023–2025
Our Penetration Testing Methodology
A rigorous, six-phase process aligned to OWASP, PTES, and NIST frameworks — delivering consistent, thorough, and defensible results on every engagement.
OSINT, footprinting, architecture discovery, and attack surface mapping to establish a comprehensive foundation.
Identify threat actors, attack vectors, and high-value assets. Prioritise testing scope based on business risk.
Automated scanning augmented with deep manual testing to catalogue every exploitable weakness in the application.
Controlled real-world attack simulations to validate exploitability, determine blast radius, and gauge actual business impact.
Privilege escalation, lateral movement analysis, and data exposure mapping to quantify the full compromise potential.
Executive summary, technical findings, severity ratings, CVSS scores, and prioritised remediation roadmap with retest support.
Every finding rated with CVSS v3.1 scoring — Critical, High, Medium, Low — to streamline your remediation prioritisation.
After remediation, we verify all fixes at no additional cost and issue a formal VAPT Certificate upon successful closure.
Live access to findings, remediation status tracking, and historical reports through an encrypted client dashboard.
Internal & External Penetration Testing
We offer both internal and external assessments, providing complete 360° coverage of your application's attack surface from every threat perspective.
Internal Pentest
Simulates a malicious insider or a compromised internal account. We assess from within your network perimeter to expose weaknesses that external scanners can never reach — misconfigurations, insecure APIs, over-privileged roles, and trust boundary violations.
External Pentest
Replicates a skilled external adversary targeting your public-facing application with zero prior knowledge. Every internet-exposed endpoint, API, authentication mechanism, and third-party integration is assessed against real-world attack techniques.
What We Assess
Our assessment scope is customised to your application's architecture and business criticality — from authentication flows and API endpoints to business logic and third-party integrations. We test what matters to your organisation.
Black Box, Grey Box & White Box Testing
Select the engagement model that best matches your threat profile, timeline, and budget — or let our experts recommend the optimal approach.
- Most realistic external attacker simulation
- Zero prior access or application knowledge
- Evaluates public-facing attack surface comprehensively
- Ideal for pre-launch and compliance validation
- Balances thoroughness with efficiency
- Partial access mirrors privileged user threats
- Uncovers both internal and external weaknesses
- Optimal cost-to-coverage ratio — our recommendation
- Complete access: source code, architecture, credentials
- Maximum vulnerability coverage — nothing missed
- SAST, DAST & IAST methodologies combined
- Ideal for high-assurance and regulated environments
Not sure which approach is right for you?
Get a Free Consultation →OWASP Top 10 — Full Coverage Guaranteed
Every engagement is benchmarked against the OWASP Top 10, the definitive industry standard for web application security risks. Our testing covers each category comprehensively.
The Highest Standard of Pentesting
We don't just meet industry benchmarks — we help define them. Our quality assurance framework ensures every engagement delivers consistent, defensible, and actionable results.
CCV-Pentesting Trustseal
Fully compliant with CCV's rigorous penetration testing standards, one of the most demanding quality marks in the industry. Every engagement is auditable.
Meticulous Documentation
Every finding is documented with reproduction steps, evidence, business impact, CVSS scoring, and actionable remediation guidance — not just a checklist.
OSCP-Certified Specialists
Every security engineer on your engagement holds current OSCP certification. No juniors, no trainees — elite hands-on practitioners from day one.
Free Retest & VAPT Certificate
We verify every remediation at no additional cost. Upon successful closure, we issue a VAPT Certificate — a trusted credential for clients and stakeholders.
Frequently Asked Questions
Everything you need to know about our web application penetration testing service.
Our Partner's
GET STARTED
Fast-track your penetration testing
Start testing in 24 hours. Connect directly with our security experts. And centralize your testing with InfoSec Brigade
Connect With Us