Evaluate Security Controls. Identify Gaps. Strengthen Governance.
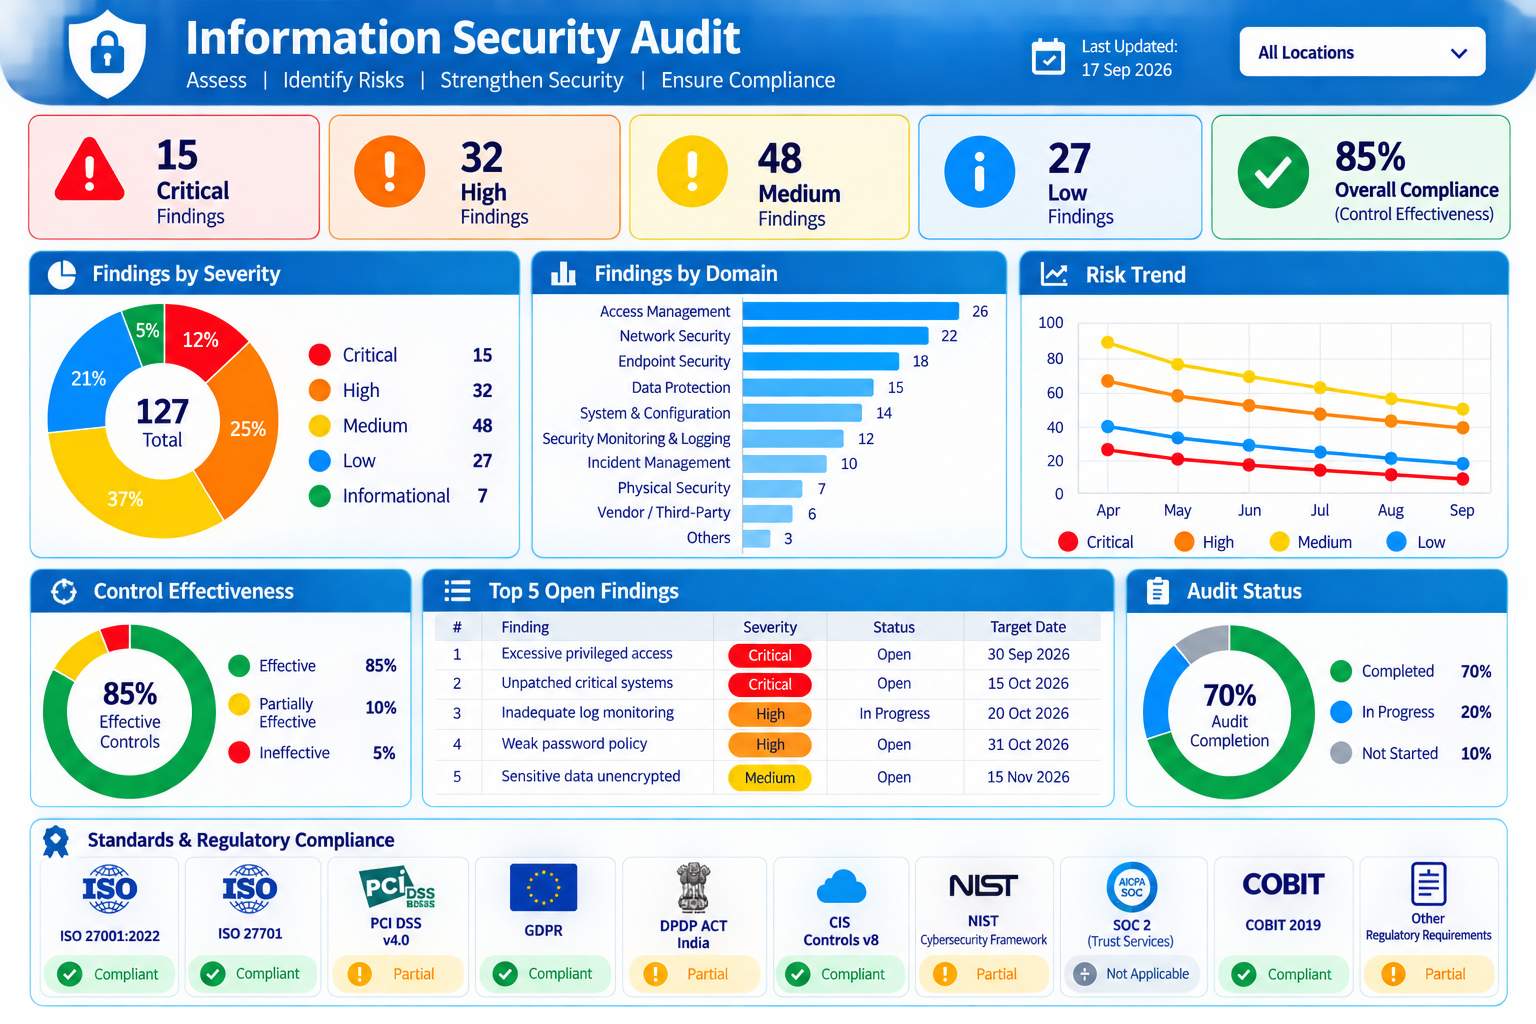
Assess your organization’s information security controls, policies, and processes. Our information security audit helps identify risks, improve governance, and align security practices with industry standards.
Identify information security gaps
Information Security Audit focuses on evaluating an organization’s security policies, processes, and controls to identify vulnerabilities, risks, and compliance gaps that could impact data protection and business operations. Organizations must regularly assess their information security framework to ensure confidentiality, integrity, and availability of critical assets. With evolving cyber threats, businesses must adopt continuous monitoring, risk assessment, and remediation strategies.
Information security auditing is not just a compliance activity—it is a strategic necessity
to identify risks, strengthen controls, and ensure effective protection of organizational assets.
Detect weaknesses in policies, processes, and controls that could lead to security breaches. Assess the effectiveness of existing controls across systems and processes. Ensure proper protection of sensitive data and business-critical information. Align security practices with industry standards and regulatory requirements. Minimize exposure to threats through timely identification and remediation. Enhance overall resilience against evolving cyber threats and attacks.Why Information Security Audit is Critical
Identify Security Gaps
Evaluate Security Controls
Protect Critical Assets
Ensure Compliance
Reduce Security Risks
Strengthen Security Posture
Improve security governance and compliance
Strengthen risk management, access controls, and security practices to align with industry standards and business requirements.
WHY INFOSEC
The smarter path to stronger security governance

Security Governance Expertise
- Assess policies and security controls.
- Identify governance gaps.
- Strengthen information security practices.
Risk-Based Security Review
- Evaluate risk management processes.
- Review access and control mechanisms.
- Improve overall security posture.
Actionable Audit Reporting
- Deliver structured audit reports.
- Provide remediation guidance.
- Support continuous security improvement.
Our Partner's
GET STARTED
Start your information security audit
Evaluate your organization’s information security controls and improve governance. Identify risks, strengthen policies, and enhance your overall security posture.
Connect With Us