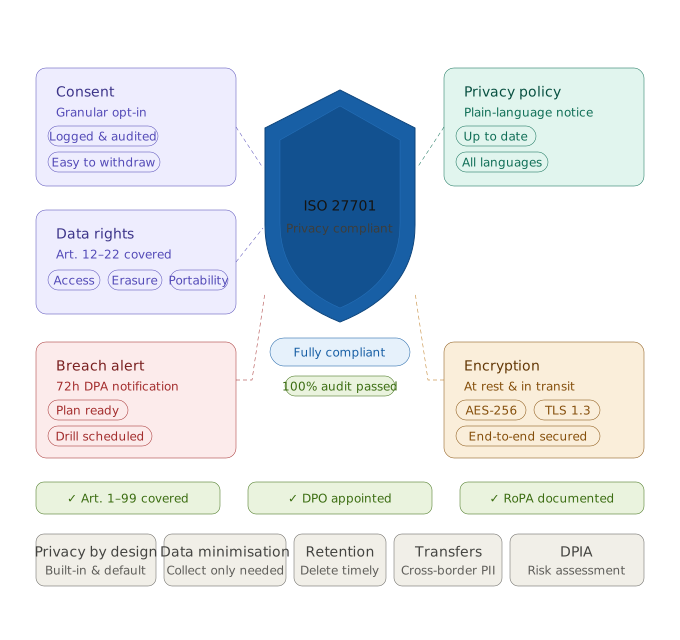
Strengthen Privacy Management. Protect Personal Data. Achieve ISO 27701 Certification.
Implement a privacy information management system aligned with ISO 27701. We help organizations extend their ISO 27001 framework, manage personal data responsibly, and achieve certification through structured consulting and audit readiness.
Implement a privacy information management system
Establish policies and controls to manage personal data in line with ISO 27701 requirements. Improve transparency, accountability, and data protection practices across your organization.
Robust Privacy Management
ISO 27701 extends your ISMS with a Privacy Information Management System (PIMS), providing a structured framework to identify, manage, and reduce privacy risks across the data lifecycle.
Builds Data Subject Confidence
As privacy expectations grow globally, ISO 27701 certification demonstrates a genuine commitment to protecting personal data — fostering trust with customers, partners, and regulators alike.
Accelerates GDPR & Regulatory Alignment
The standard maps directly to GDPR, CCPA, and other major privacy regulations, providing a structured path to compliance and significantly reducing the risk of regulatory penalties.
Defines Controller & Processor Roles
ISO 27701 clearly distinguishes obligations for both data controllers and processors, helping organizations manage third-party relationships and supply chain privacy risk with confidence.
Streamlines Privacy Operations
By formalizing privacy workflows — from consent management to breach response — ISO 27701 reduces operational complexity and enables teams to respond to privacy incidents faster and more consistently.
Competitive Privacy Advantage
Privacy-first organizations earn a genuine market edge. Certification opens doors to enterprise clients and public sector contracts where demonstrable data protection is a prerequisite.
Seamless ISO 27001 Extension
Built as a direct extension of ISO 27001, the standard integrates into your existing ISMS — avoiding duplicate effort and leveraging security governance already in place.
Audit-Ready Privacy Records
The framework mandates comprehensive records of processing activities (RoPA), PIAs, and consent evidence — ensuring you are always prepared for regulatory audits or data subject requests.
Reduces Financial & Reputational Risk
Proactive privacy controls prevent costly data breaches and regulatory fines. Organizations implementing ISO 27701 consistently report lower incident costs and stronger reputational resilience over time.
Our proven approach
How Can We Help You with ISO 27701?
Whether you are starting your ISO 27701 journey or looking to strengthen an existing privacy programme, our specialists provide end-to-end support tailored to your organisation. Select a service area to learn more.
WHY INFOSEC
Smarter path to Privacy Compliance
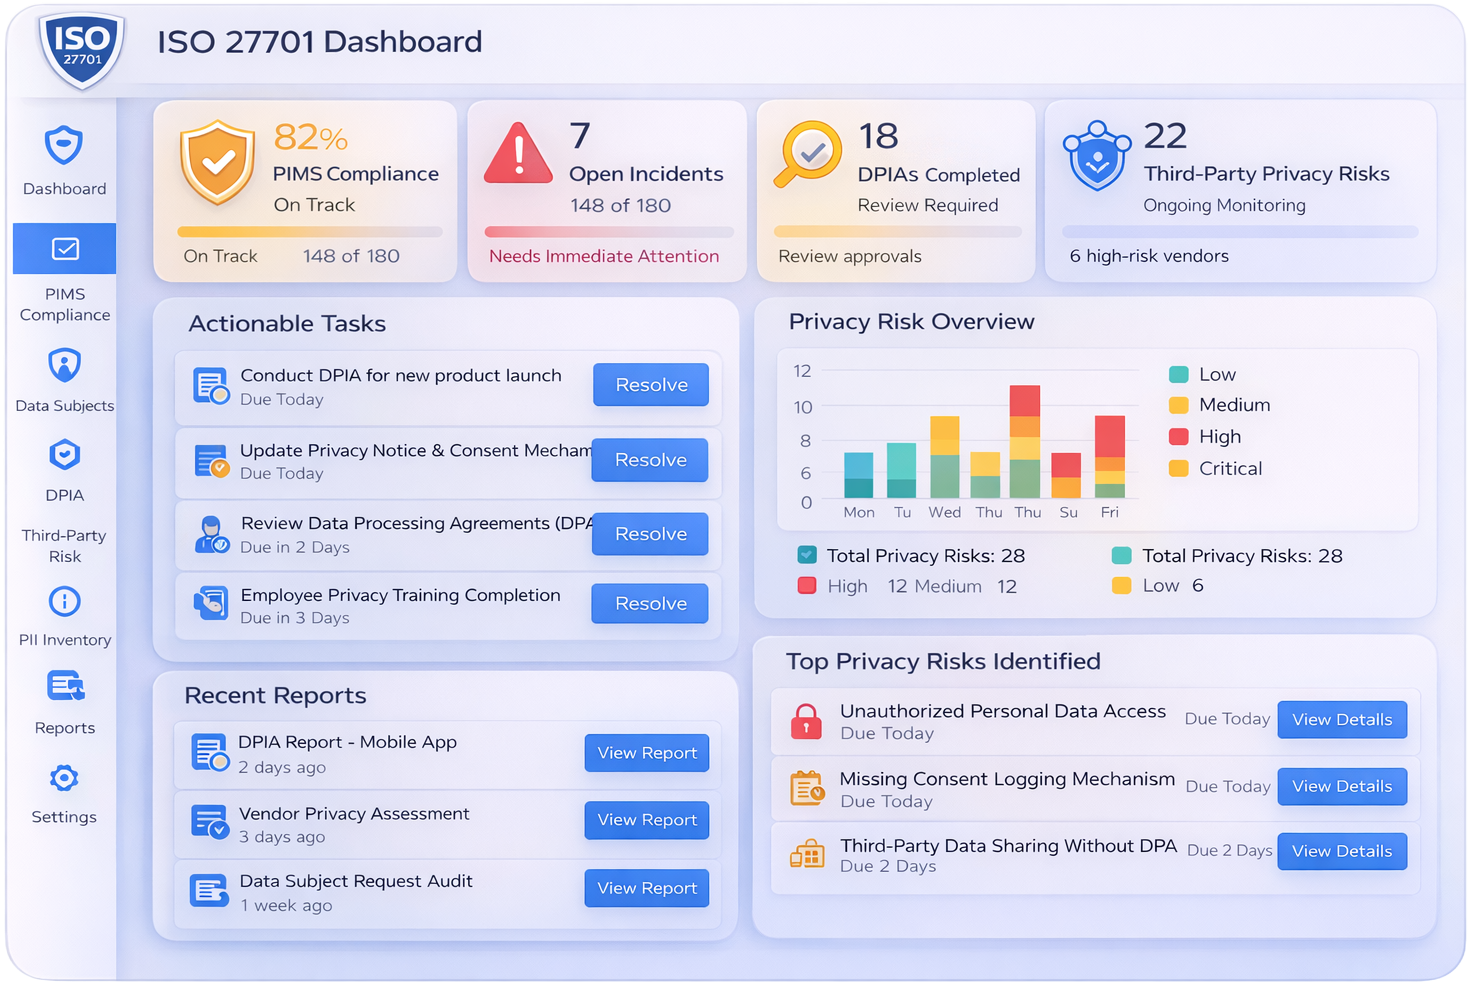
Privacy Compliance Expertise
- Align privacy practices with ISO 27701 requirements.
- Identify gaps in personal data protection.
- Provide structured remediation guidance.
Privacy Governance Framework
- Implement privacy policies and controls.
- Define roles and responsibilities.
- Strengthen data protection governance.
Certification Readiness Support
- Prepare for ISO 27701 audits.
- Improve documentation and controls.
- Support certification success.
Our Partner's
GET STARTED
Start your ISO 27701 certification journey
Strengthen privacy management and achieve ISO 27701 certification. Implement controls, improve governance, and protect personal data across your organization.
Connect With Us