Infosec Brigade

Cloud Penetration Testing by Experts

Adversarial security assessments across AWS, Azure, and Google Cloud — uncovering misconfigurations, IAM flaws, exposed storage, and lateral movement paths before attackers do.
Cloud Penetration Testing | Elite Security Services
ISO 27001:2022 Certified
AWS · Azure · GCP Certified
OSCP & CCSP-Certified Team
24/7 Incident Response
VAPT Certificate Issued

What is Cloud Penetration Testing?

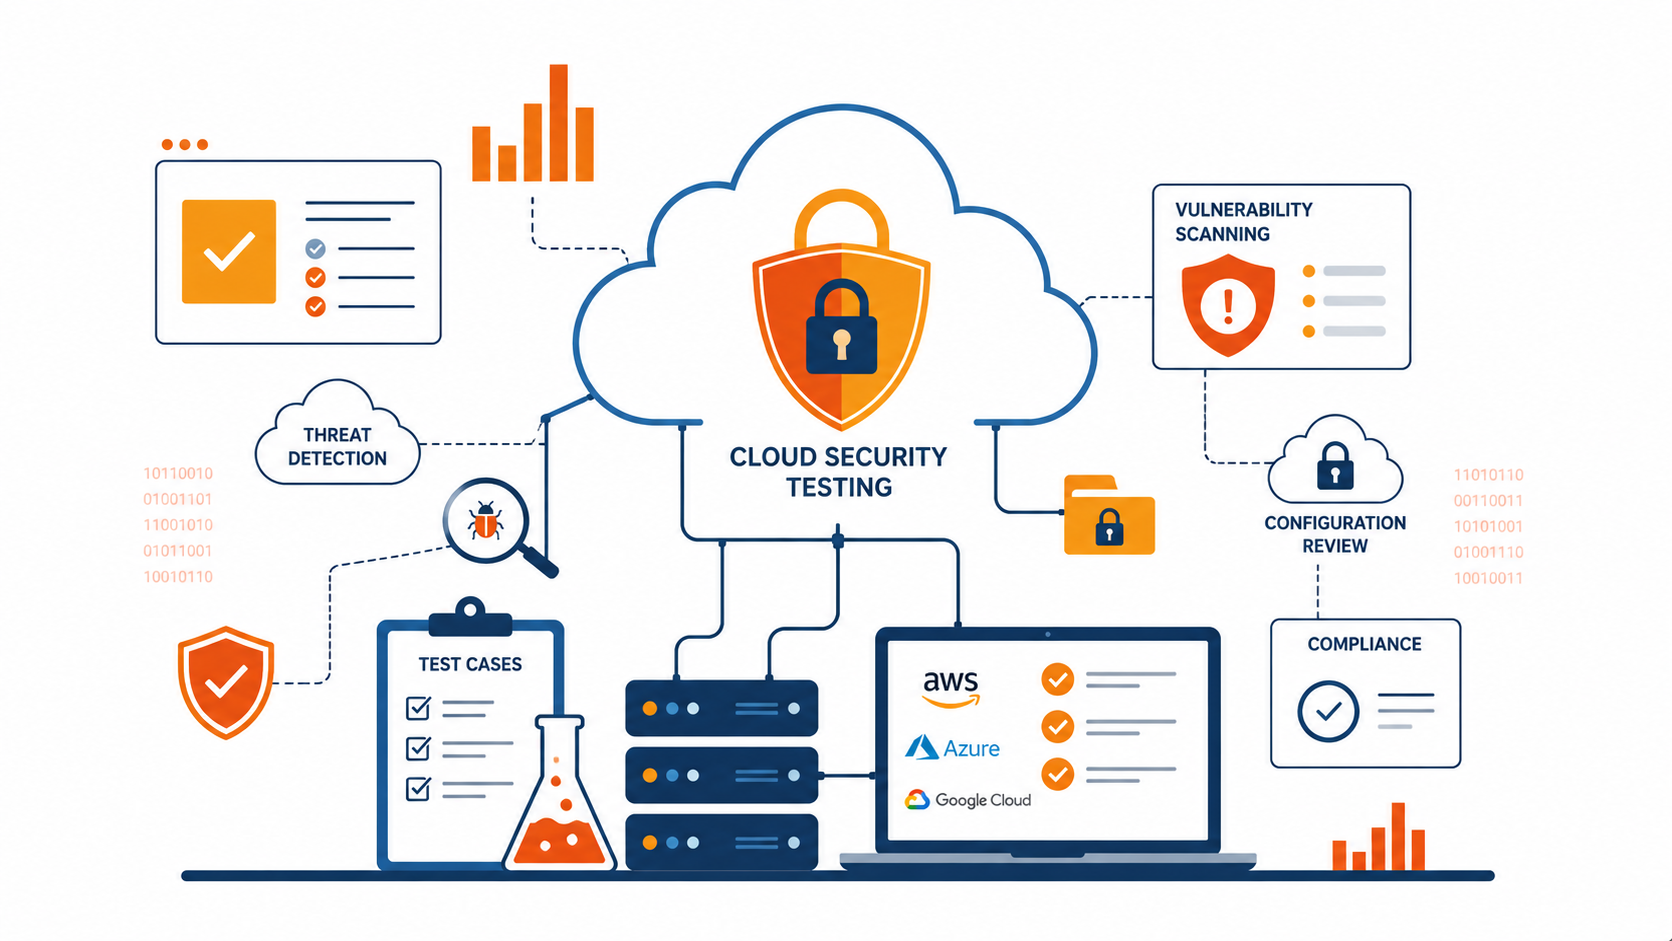
Cloud Penetration Testing is a hands-on adversarial assessment of your cloud infrastructure — covering identity and access management, storage exposure, network controls, serverless functions, container orchestration, and cross-tenant attack paths — across AWS, Azure, and Google Cloud Platform.

Our certified cloud security engineers go far beyond automated compliance scanners. We manually exploit misconfigured IAM policies, overprivileged service accounts, publicly exposed buckets, insecure APIs, and vulnerable CI/CD pipelines to uncover real-world attack chains before malicious actors do.

  • ☁️
    Multi-Cloud & Hybrid Coverage Comprehensive assessments across AWS, Azure, GCP, and hybrid cloud environments — no blind spots across your entire cloud estate.
  • 🏅
    Compliance Assurance Meet SOC 2, ISO 27001, PCI-DSS, HIPAA, and CSA CCM requirements with documented evidence of cloud security validation.
  • 🔐
    IAM & Privilege Escalation Testing Identify overprivileged roles, misconfigured trust policies, and lateral movement paths that allow attackers to escalate to cloud administrator.
  • Zero Operational Disruption All testing is conducted using read-only recon and controlled exploitation in coordination with your team — your production workloads remain fully protected.
Top Cloud Vulnerability Distribution
IAM Misconfiguration & Privilege Escalation88%
Publicly Exposed Storage (S3 / Blob / GCS)74%
Secrets & Credentials in Code / Metadata66%
Insecure Security Group / Firewall Rules59%
Vulnerable Serverless & Container Configs51%
Unencrypted Data & Logging Gaps44%

Cloud Pentest Methodology

A structured, 6-phase engagement aligned with CSA Cloud Controls Matrix, NIST SP 800-144, and CIS Cloud Benchmarks — delivering complete cloud attack surface coverage.

01
📋
Scoping & Authorization
Define cloud accounts, regions, services, and blast radius. Obtain written authorization and establish emergency contacts.
02
🔍
Cloud Reconnaissance
Enumerate cloud assets, services, IAM entities, exposed endpoints, and metadata via OSINT and non-intrusive API enumeration.
03
🗺️
Attack Surface Mapping
Map IAM permission graphs, network topologies, trust relationships, and data flows to identify high-value attack paths.
04
⚔️
Exploitation
Manually exploit IAM misconfigurations, exposed storage, SSRF, secrets leakage, and container escape with controlled, non-destructive techniques.
05
📈
Lateral Movement & Escalation
Simulate post-compromise pivoting across accounts, VPCs, and services — validating blast radius and segmentation controls.
06
📄
Reporting & Remediation
Deliver executive summary, technical report with CVSS-scored findings, attack path diagrams, and prioritised remediation roadmap within 72 hours.

AWS, Azure & Google Cloud — Full Coverage

Our certified engineers deliver deep, platform-native assessments for every major cloud provider — not generic checklists.

Amazon Web Services

AWS Penetration Testing

Deep assessment of your AWS environment covering IAM privilege escalation, S3 bucket exposure, EC2 metadata SSRF, Lambda function abuse, cross-account trust exploitation, and CloudTrail evasion. Aligned to AWS Foundational Security Best Practices and CIS AWS Benchmark.

IAM & STS Abuse S3 Bucket Exposure EC2 / EKS / Lambda Cross-Account Attacks CloudTrail Evasion Secrets Manager
Microsoft Azure

Azure Penetration Testing

Comprehensive Azure assessment covering Entra ID (formerly AAD) misconfigurations, RBAC privilege escalation, Blob Storage exposure, Service Principal abuse, Azure Functions security, AKS cluster attack paths, and Key Vault access weaknesses.

Entra ID / AAD RBAC Escalation Blob Storage AKS & Functions Service Principals Key Vault Abuse
Google Cloud Platform

GCP Penetration Testing

Full GCP assessment targeting IAM policy misconfigurations, service account key abuse, GCS bucket exposure, metadata server SSRF, GKE cluster security, Cloud Functions privilege escalation, and VPC firewall bypass techniques.

IAM & Service Accounts GCS Bucket Exposure GKE Cluster Attacks Metadata SSRF Cloud Functions VPC Firewall Rules

Black Box, Grey Box & White Box Cloud Testing

Choose the engagement model that matches your threat profile, compliance requirements, and organisational maturity — or let our experts advise you.

Black Box
Black Box Assessment
Unauthenticated External Cloud Attack Simulation
  • Most realistic external attacker perspective
  • Zero prior cloud account access or credentials
  • Targets publicly exposed services and storage
  • Ideal for pre-launch and compliance validation
Grey Box
🔲
Grey Box Assessment
Authenticated Insider / Compromised Credential Model
  • Simulates phished employee or compromised access key
  • Tests IAM privilege escalation and lateral movement
  • Optimal coverage-to-cost ratio — our recommendation
  • Covers both external and authenticated attack paths
White Box
White Box Assessment
Full Architecture & Infrastructure Review
  • Full account access, IaC configs, and architecture docs
  • Maximum vulnerability coverage across all services
  • Config review + active exploitation combined
  • Ideal for regulated environments and high-assurance use

Not sure which approach fits your cloud environment?

Get a Free Consultation →

Cloud Attack Surface — Full Coverage Guaranteed

Every engagement benchmarked against CSA CCM, CIS Cloud Benchmarks, and NIST SP 800-144. We assess every exploitable layer of your cloud environment.

🔑
Identity
IAM, Roles & Privilege Escalation
🪣
Storage
S3 / Blob / GCS Bucket Exposure
🌐
Network
Security Groups & VPC Misconfig
🔒
Secrets
Secrets, Keys & Credential Leakage
📦
Containers
EKS / AKS / GKE Cluster Security
Serverless
Lambda / Functions / Cloud Run
🔗
APIs
API Gateway & Service Mesh
🏗️
IaC
Terraform / CloudFormation Review
🔄
CI/CD
Pipeline & Supply Chain Security
🗄️
Database
RDS / CosmosDB / Cloud SQL Exposure
👁️
Logging
CloudTrail / Monitor / Audit Log Gaps
🌉
Cross-Cloud
Cross-Account & Tenant Pivoting

The Highest Standard of Cloud Pentesting

We don't just tick compliance checkboxes — we emulate real adversaries to expose the vulnerabilities that automated tools and scanner-only assessments consistently miss.

🏅

CCV-Pentesting Trustseal

Fully compliant with CCV's rigorous penetration testing quality standards — one of the most demanding quality marks in the industry. Every cloud engagement is fully auditable.

📄

Meticulous Documentation

Every finding includes cloud-native attack path diagrams, console/CLI evidence, CVSS v3.1 scoring, business impact analysis, and prioritised remediation with Terraform/IaC fixes.

👨‍💻

OSCP & CCSP-Certified Specialists

Every engineer holds current OSCP and Certified Cloud Security Professional (CCSP) certifications alongside platform-native AWS, Azure, and GCP security credentials. No juniors.

🔄

Free Retest & VAPT Certificate

We verify every cloud remediation at no extra cost. Upon successful closure, we issue a VAPT Certificate — a trusted credential for auditors, regulators, and enterprise customers.

Certifications & Standards
🛡️ ISO 27001:2022
☁️ CSA CCM
🏆 CCV Pentest Certified
🔐 CCSP Certified Team
📋 NIST SP 800-144
📏 CIS Cloud Benchmarks

Frequently Asked Questions

Everything you need to know about our Cloud Penetration Testing service across AWS, Azure, and GCP.

What is a Cloud Penetration Test? +
A Cloud Penetration Test is a targeted security assessment where our certified engineers simulate real-world attacks against your cloud infrastructure — covering IAM roles, storage buckets, compute instances, serverless functions, containers, APIs, and network controls. Unlike compliance scanners, we apply adversarial thinking to discover complex attack chains that automated tools miss, including cross-account privilege escalation and metadata server SSRF.
Does cloud pentesting require access to our live environment? +
It depends on the engagement model. Black Box testing requires no credentials — we attack from the outside as an adversary would. Grey Box and White Box testing requires a dedicated read-only IAM role or equivalent credentials with defined scope. All testing is non-destructive and carefully coordinated to avoid any impact to your production workloads.
Do AWS, Azure, and GCP allow penetration testing? +
Yes. AWS, Azure, and GCP all permit penetration testing of your own cloud resources without prior approval for most services, provided testing stays within your own accounts and complies with each provider's Acceptable Use Policy. Our team handles all required notifications and pre-engagement documentation with the cloud providers on your behalf.
What are the most common cloud vulnerabilities you find? +
The most frequent critical findings in our cloud engagements include: overprivileged IAM roles enabling privilege escalation to Administrator; publicly accessible S3/Blob/GCS buckets containing sensitive data; hardcoded API keys and secrets in Lambda functions, GitHub repos, or EC2 user data; missing MFA on privileged accounts; overly permissive security groups exposing internal services; and insecure Kubernetes RBAC allowing cluster-admin escalation.
What deliverables will we receive? +
You receive: a comprehensive technical report with all findings, CVSS v3.1 severity ratings, exploitation evidence and screenshots, and cloud-native remediation guidance (including Terraform/IaC fixes); an executive summary for board and C-suite review; attack path diagrams showing IAM escalation chains; a prioritised remediation roadmap; a free retest to verify all remediations; and a VAPT Certificate upon successful closure.
How often should we conduct a Cloud Pentest? +
We recommend annual cloud penetration testing as a baseline, with additional assessments triggered by major infrastructure changes — new cloud accounts, significant IaC refactoring, new services or regions, M&A cloud integrations, or after a security incident. Organisations subject to SOC 2, PCI-DSS, ISO 27001, or FedRAMP typically require semi-annual or quarterly assessments to maintain compliance.
GET STARTED

Fast-track Security Testing

Start testing in 24 hours. Connect directly with our security experts. And centralize your testing with InfoSec Brigade

Connect With Us